

CVE-2024-26152 json
Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
published 2024-02-22 2 y ago modified 2026-06-17 4 mo ago also EUVD-2024-0544 , GHSA-6xv9-957j-qfhg , PYSEC-2024-249
- cvss
- 4.7
- version 3.1, CNA
- cisa kev
- Not listed
- not in CISA's catalog
- epss
- 2.2%
- EPSS 2.2% chance of exploitation in 30 days, percentile 82%
- public exploits
- 0
- none known
Summary
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.
### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.
### PoC
1. Create a project. 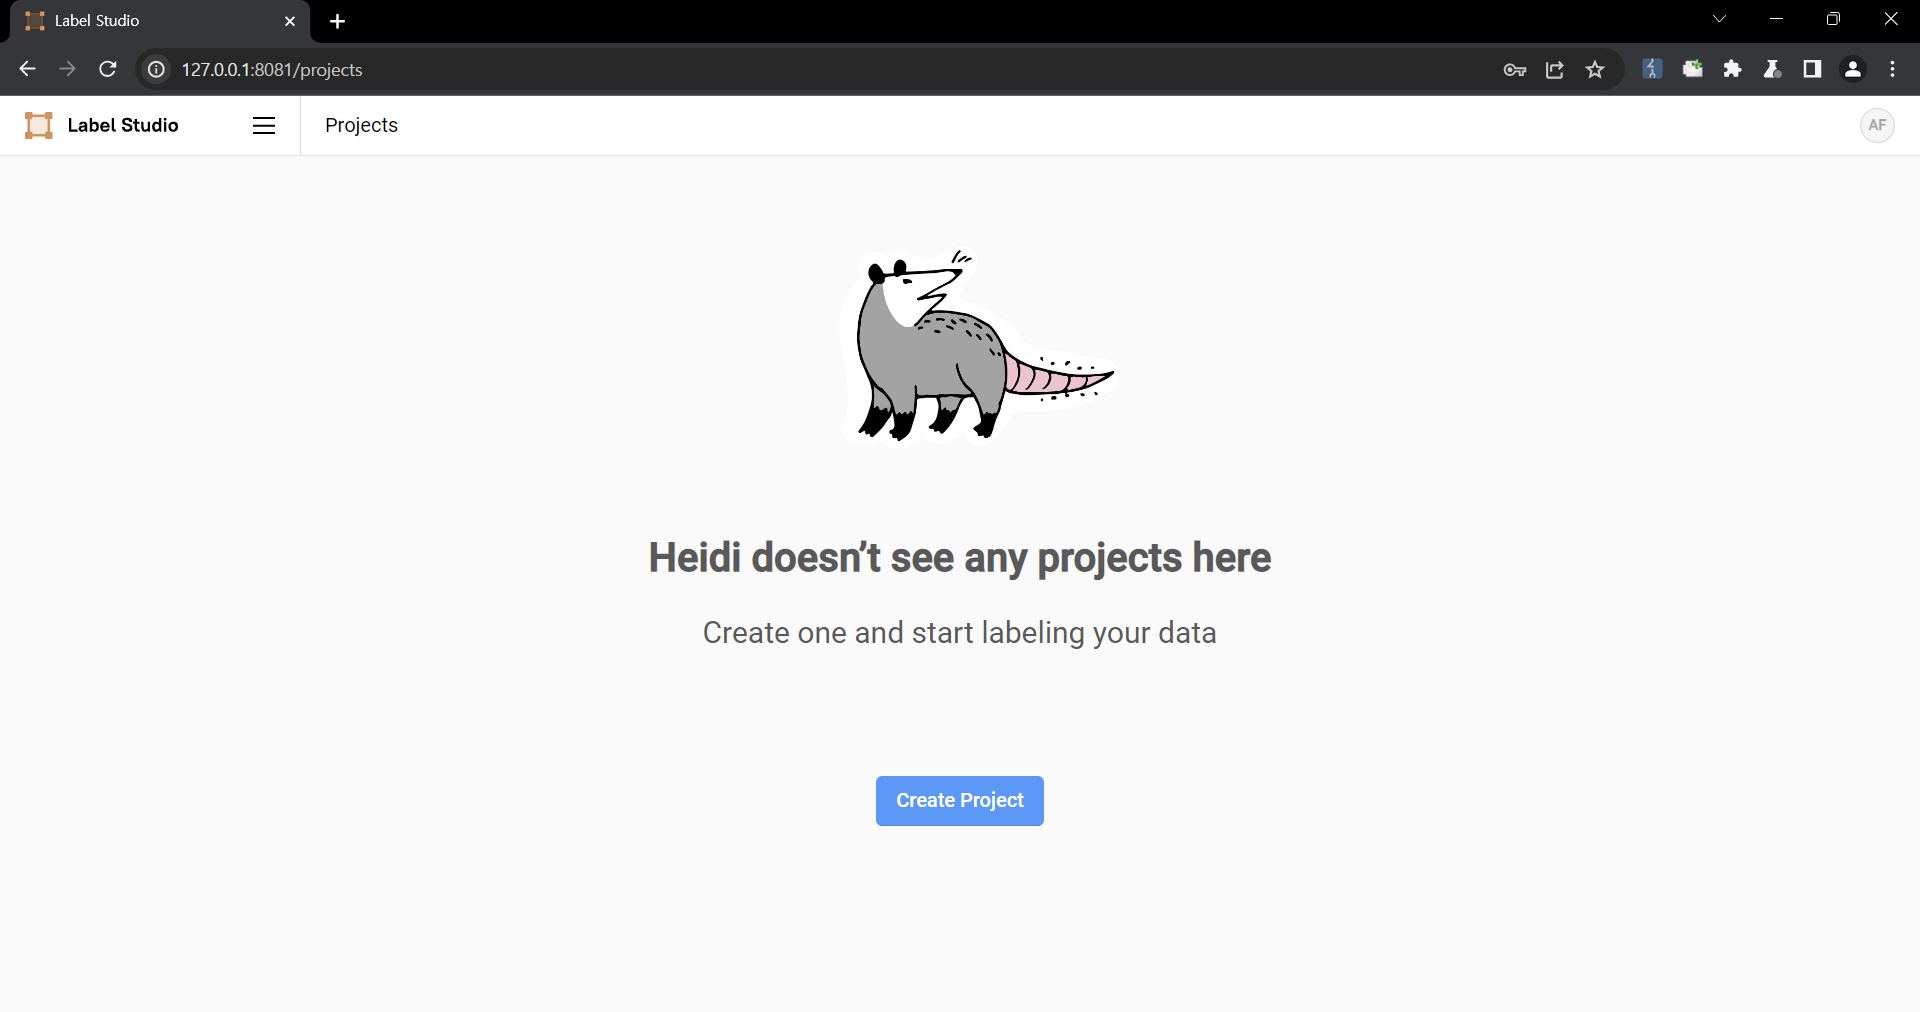
2. Upload a file containing the payload using the "Upload Files" function. 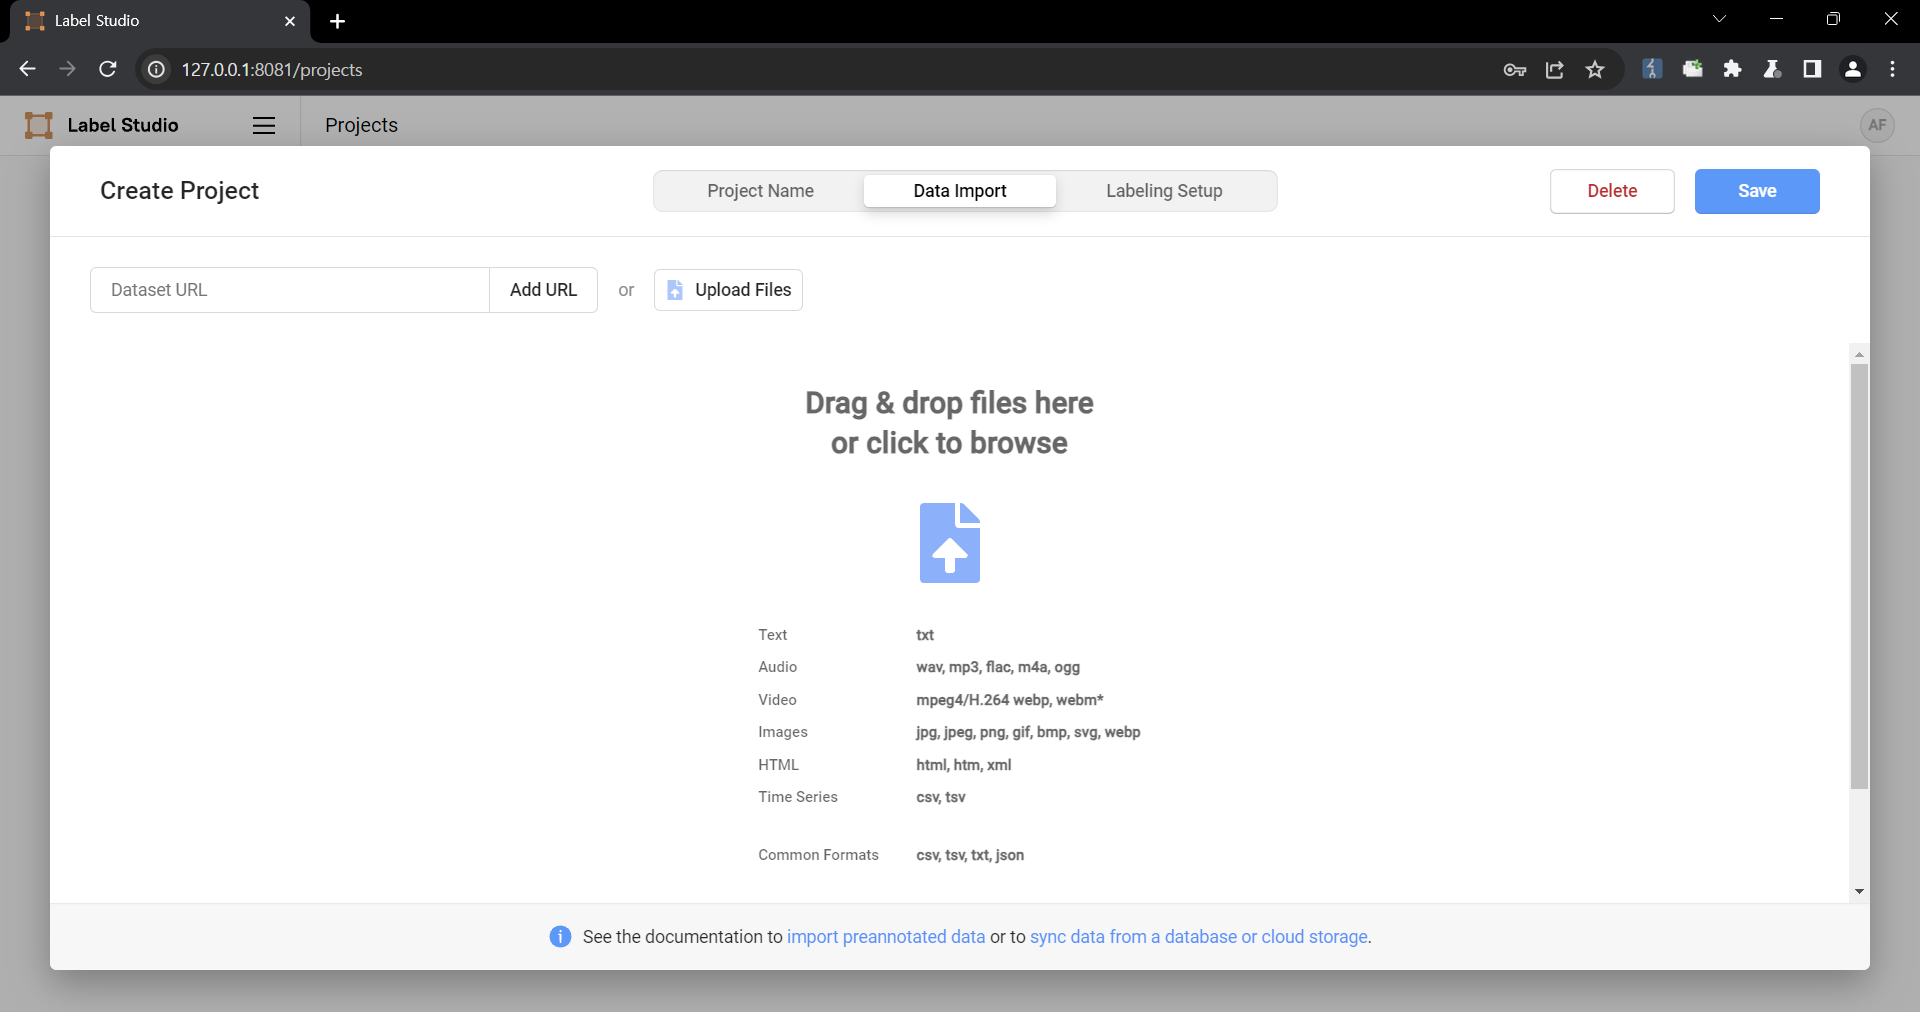 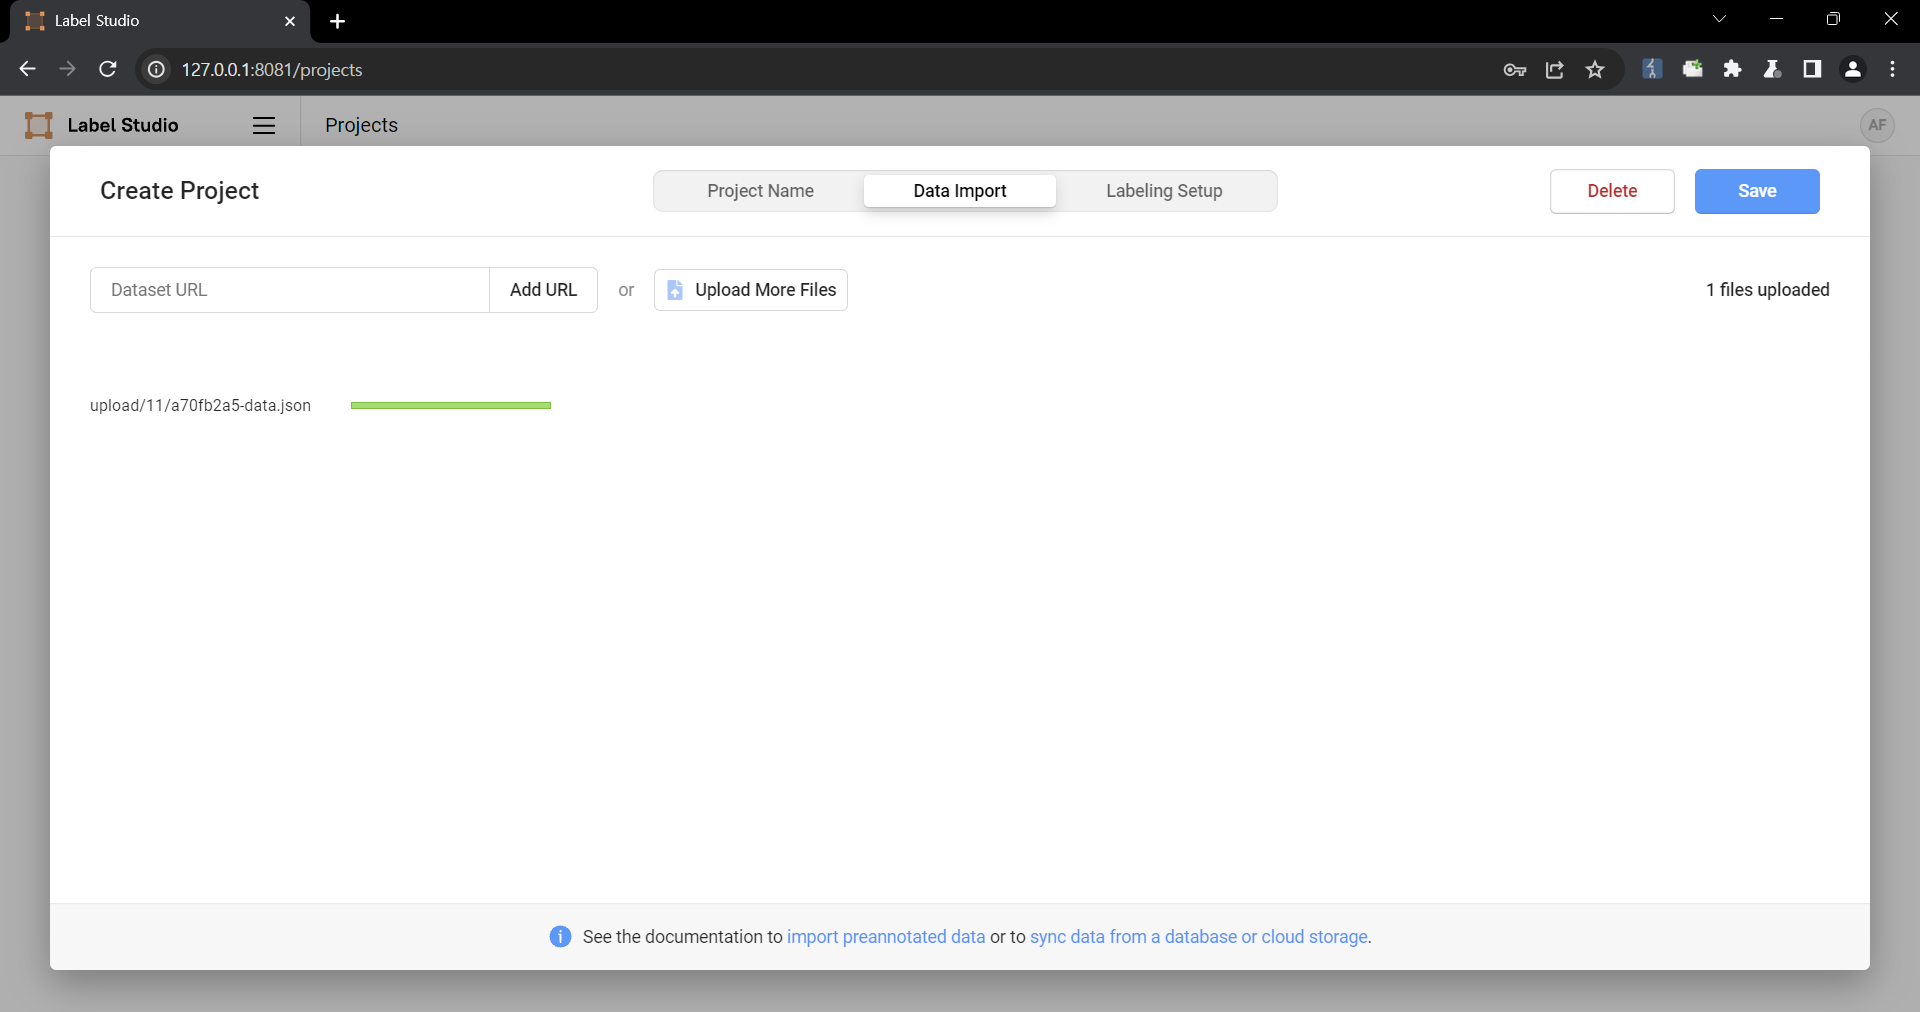
The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ```
3. Select the text-to-image generation labeling template of Ranking and scoring 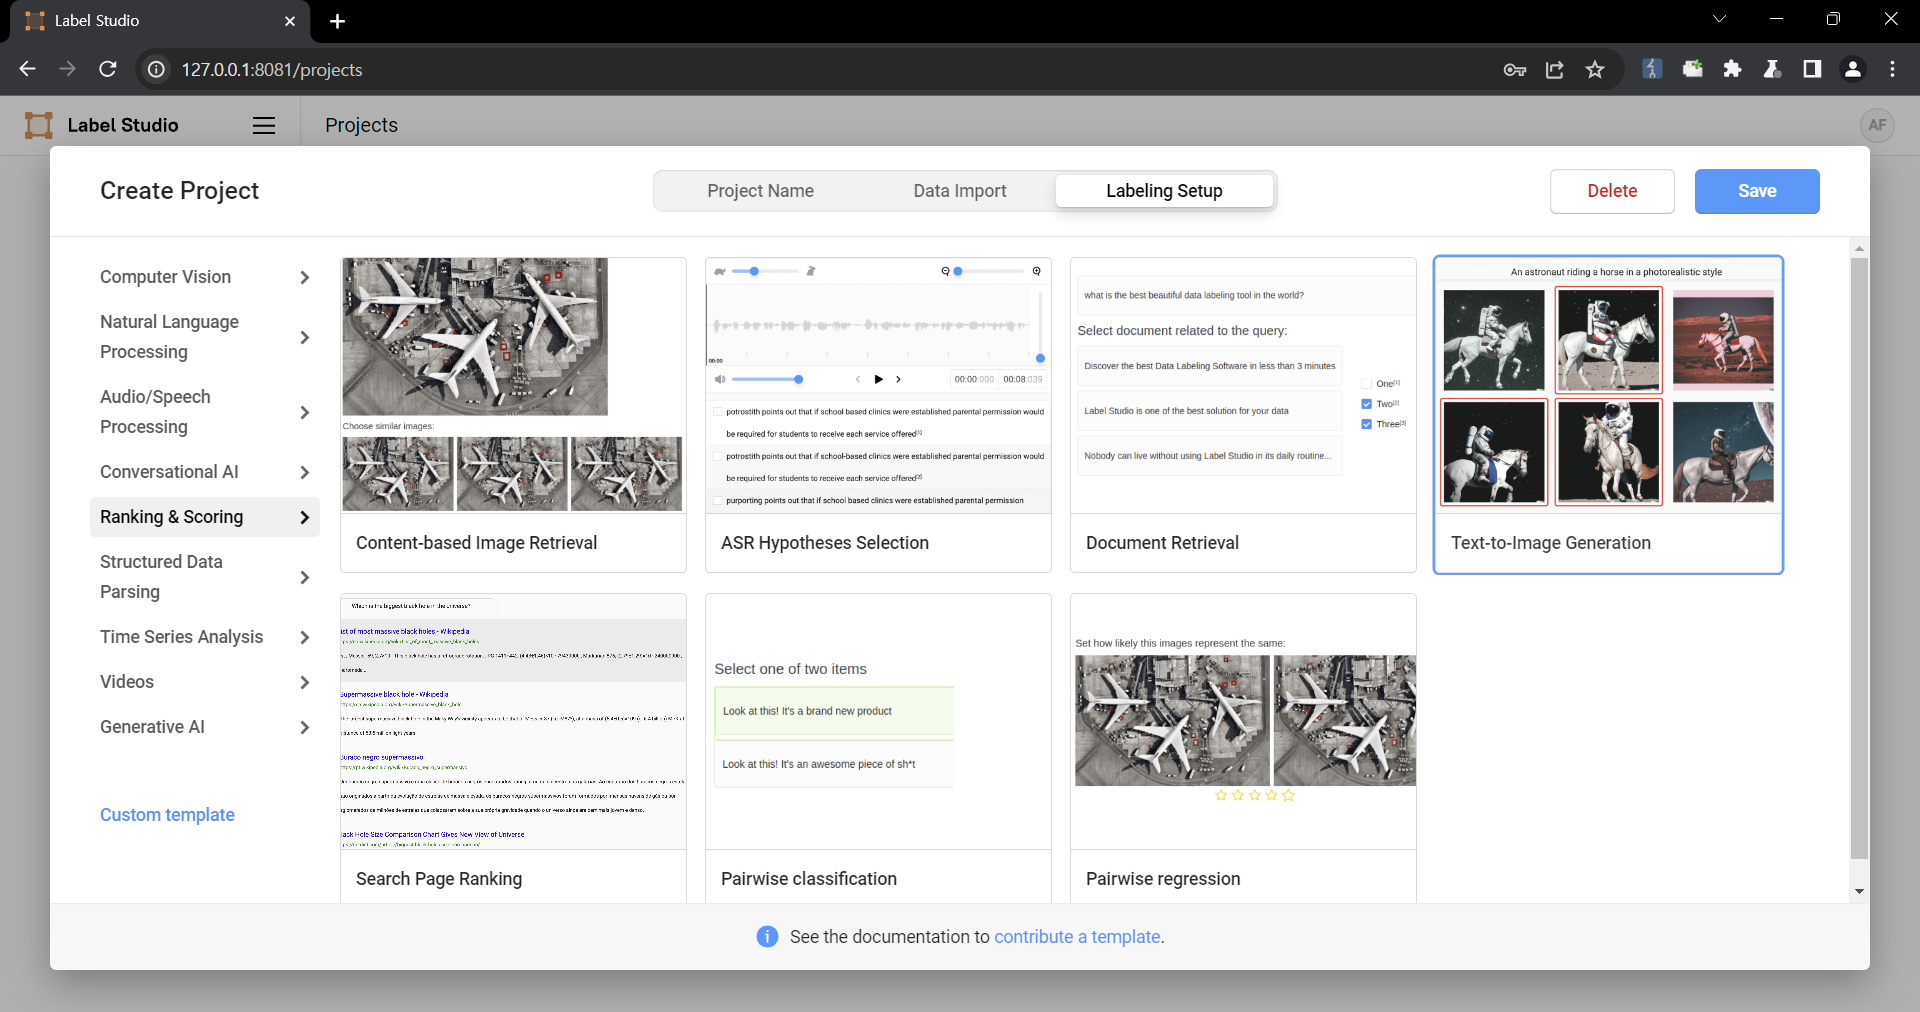 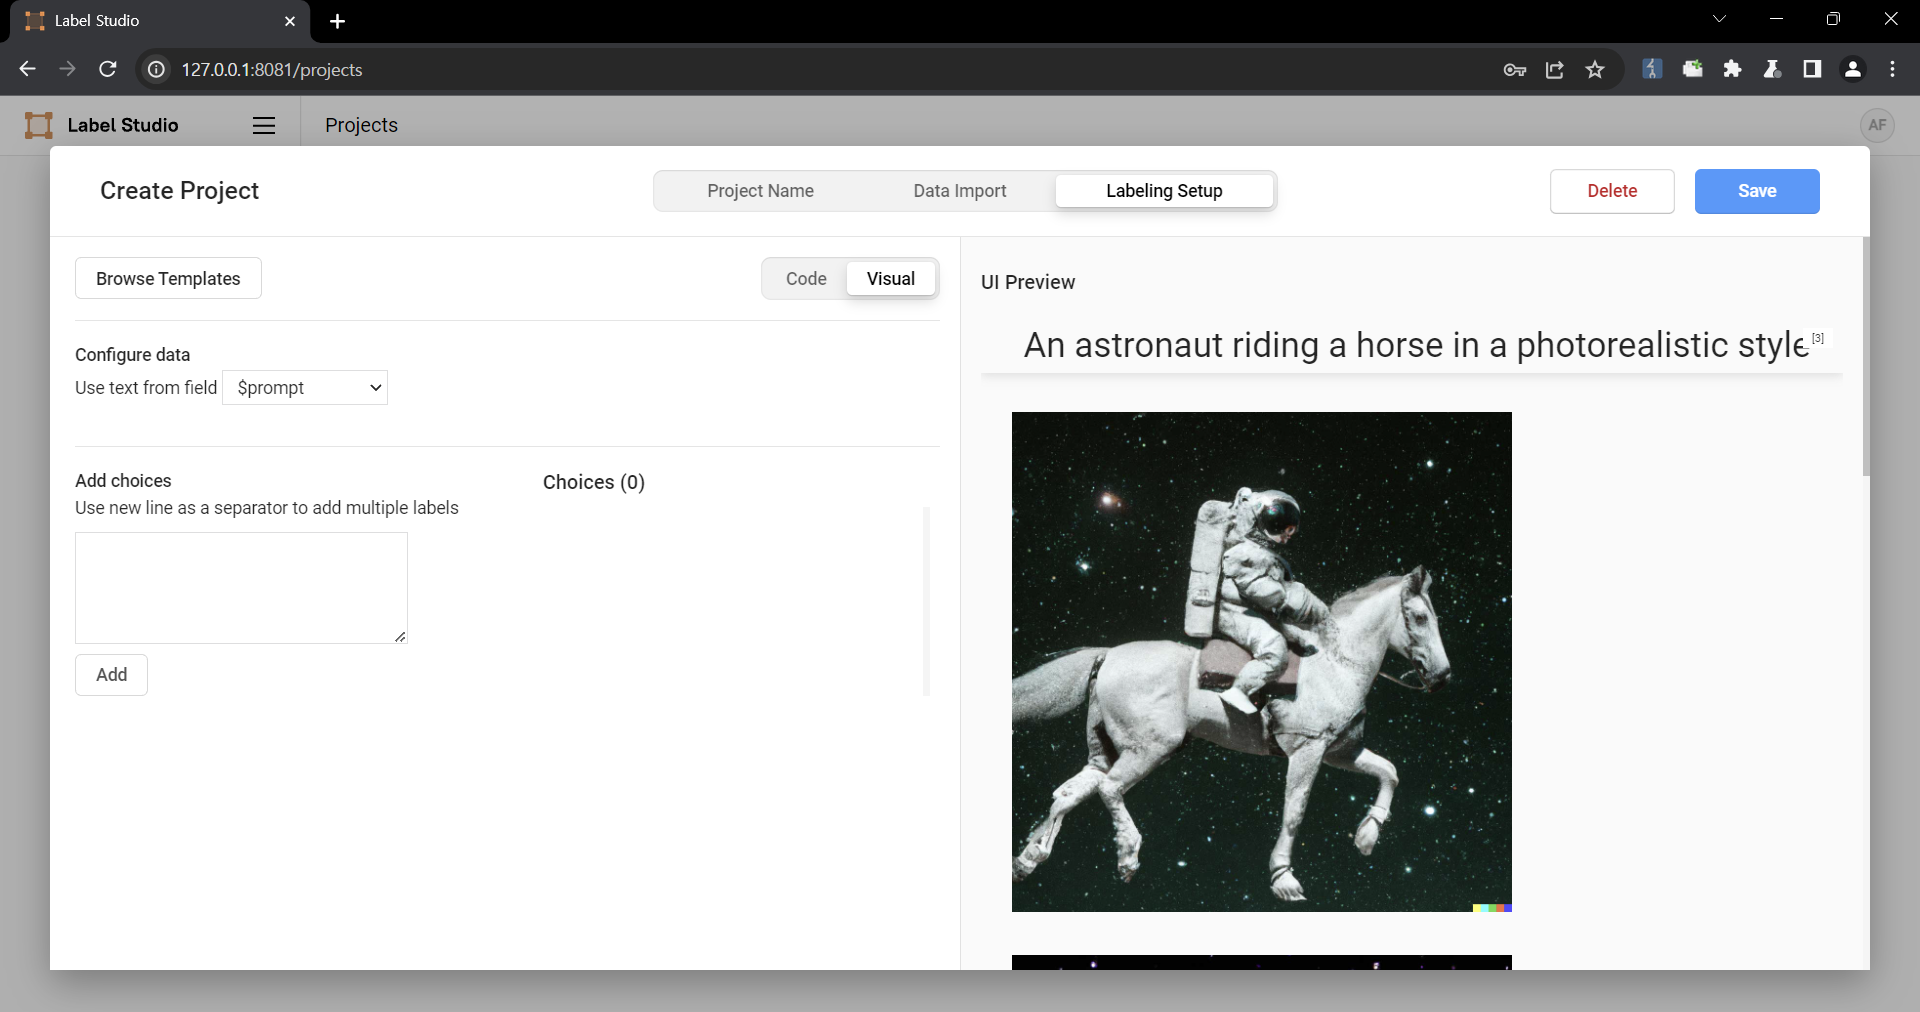
4. Select a task 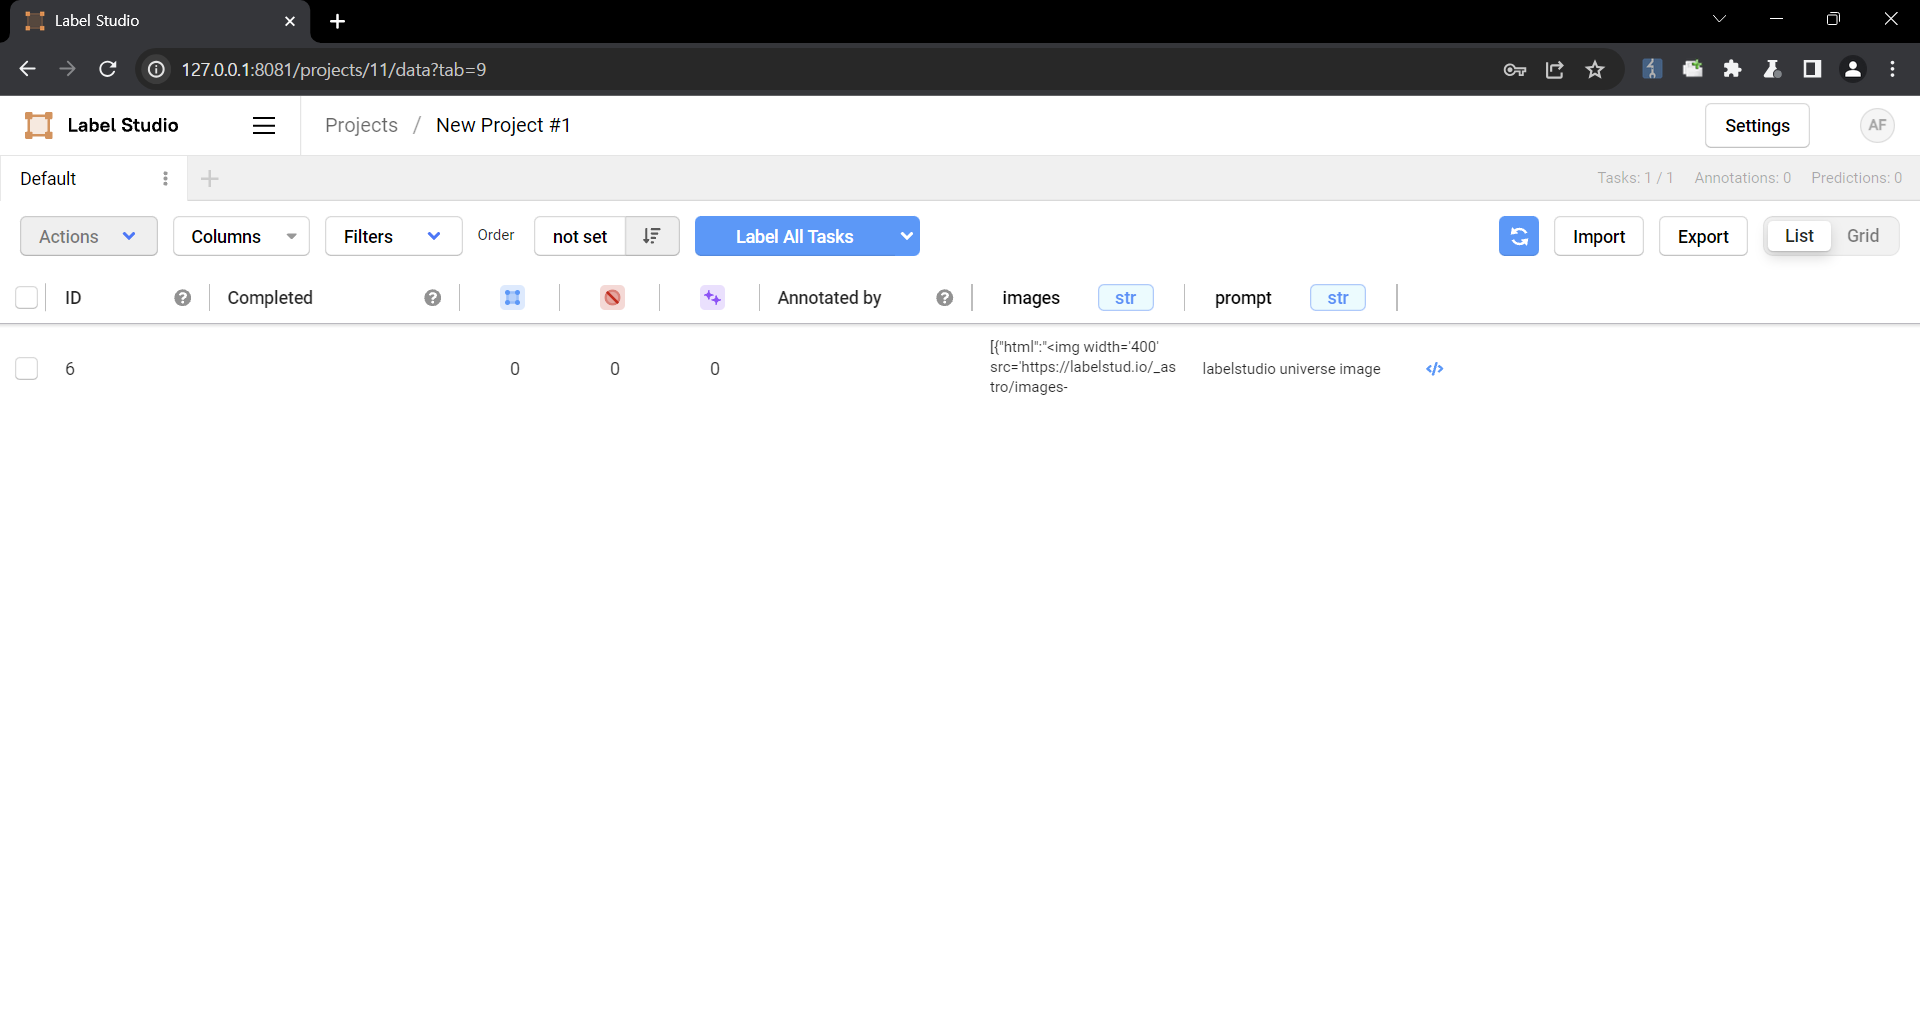
5. Check that the script is running 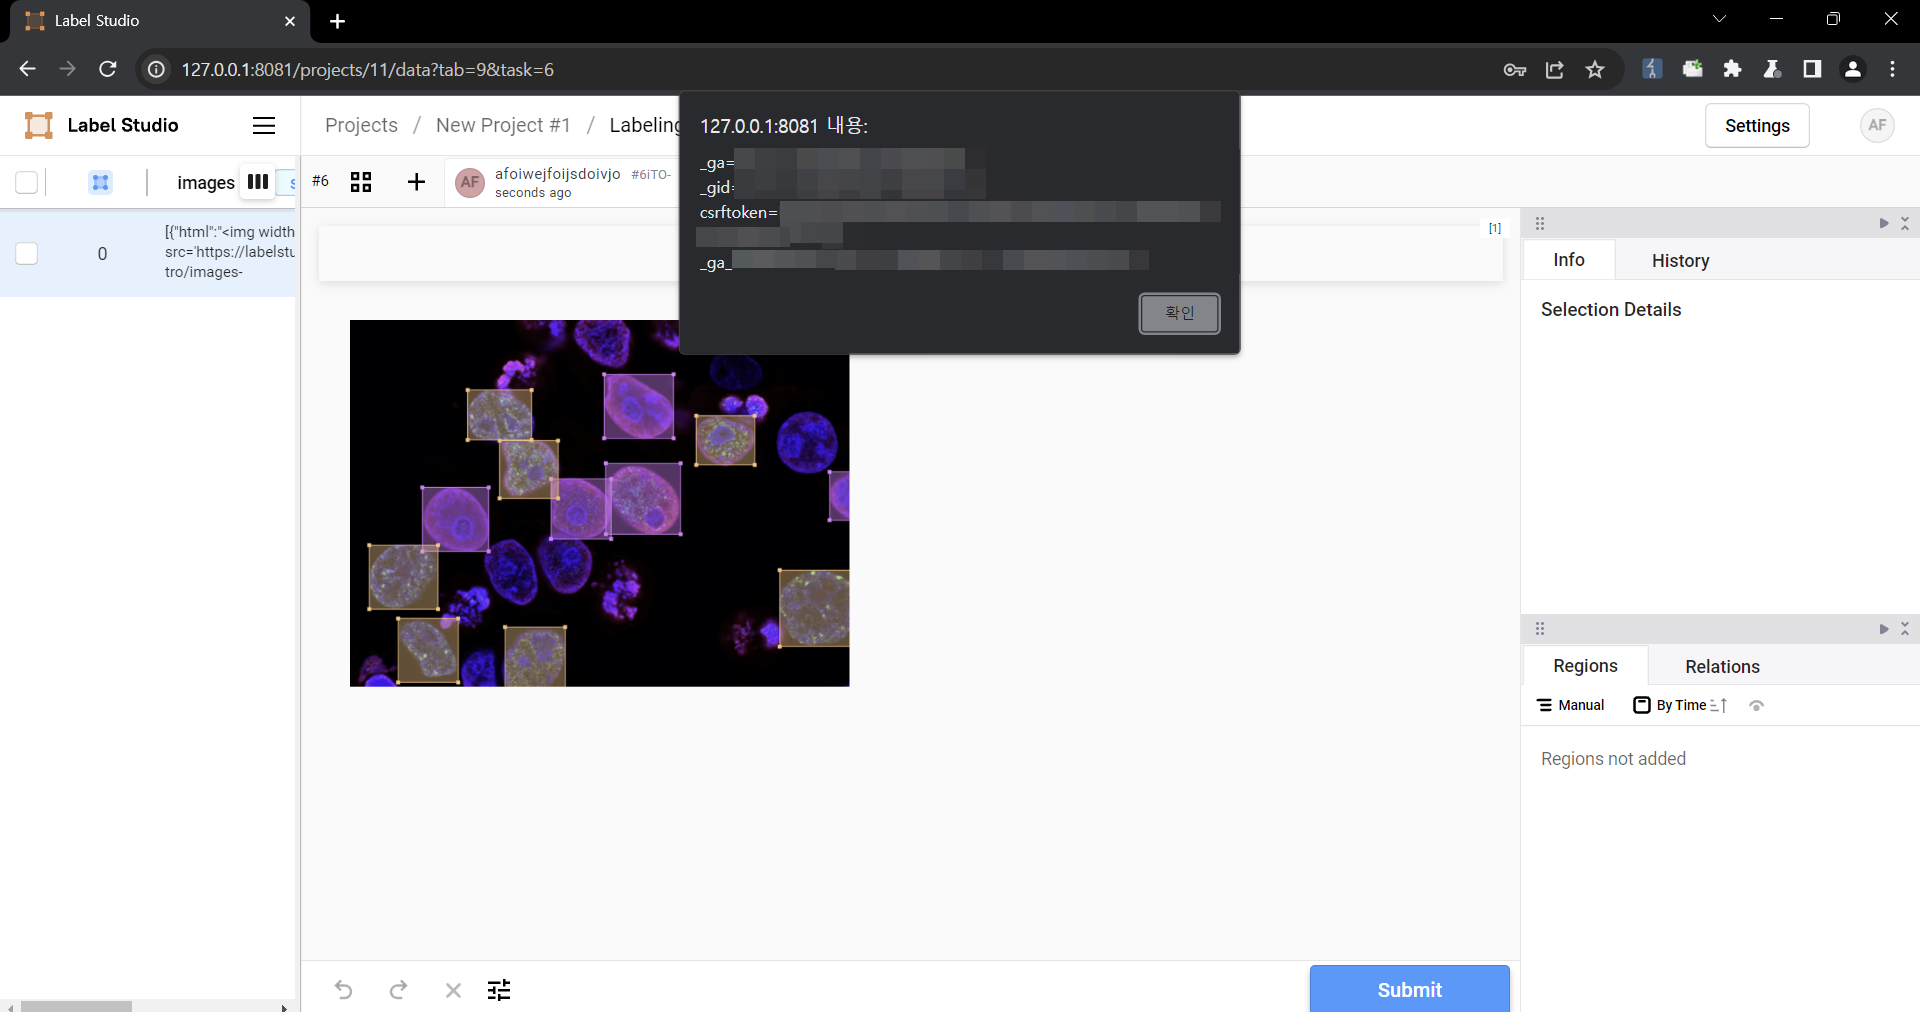
### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
Patch / fix
- pypi label-studio 1.11.0
- humansignal label_studio 1.11.0
CISA SSVC
- Exploitation
- Proof of concept is public
- Automatable
- no
- Technical impact
- partial
- Assessed
- 2 y ago
Exploit prediction
2.20% chance of exploitation in the next 30 days, higher than 82% of all scored CVEs (FIRST EPSS, 2026-11-08).
Exploits and checks
- github.com https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg referenced PoC, tagged "exploit" by a source, unverified
CVSS scores
| assigned by | version | score | vector |
|---|---|---|---|
| CNA | 3.1 | 4.7 | CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N |
| GitHub | 3.1 | 4.7 | CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N |
| NVD | 3.1 | 6.1 | CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N |
| OSV | 3.1 | 6.1 | CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N |
Affected packages
| ecosystem | package | affected | fixed in |
|---|---|---|---|
| pypi | label-studio | <1.11.0 |
1.11.0 |
Affected products
- HumanSignal label-studio
- humansignal label_studio
Classification
- Weakness
-
- CWE-79 Improper Neutralization of Input During Web Page Generation
References
-
github.com
/HumanSignal/label-studio/pull/5232
web, patch
-
github.com
/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8
web, patch
-
github.com
/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg
web, exploit, vendor-advisory, advisory, evidence
-
github.com
/HumanSignal/label-studio/releases/tag/1.11.0
web, release-notes
-
nvd.nist.gov
/vuln/detail/CVE-2024-26152
advisory
-
github.com
/HumanSignal/label-studio
package
-
github.com
/pypa/advisory-database/tree/main/vulns/label-studio/PYSEC-2024-249.yaml
web
-
github.com
/advisories/GHSA-6xv9-957j-qfhg
advisory
Sources
- CVE List CVE-2024-26152
- GitHub Advisory GHSA-6xv9-957j-qfhg
- NVD CVE-2024-26152
- OSV PYSEC-2024-249
Fencer Vulns keeps one entry per vulnerability: the CVE id wins, then GHSA, and records that alias each other are merged, except that two CVEs always keep separate entries. The same data is available as JSON.
CPEs and fixed versions use Anchore's correction of NVD's data: Added CPE configurations because not yet analyzed by NVD.